The 2026 Verizon Data Breach Investigations Report is out, and it’s time to break down what really matters for IT security teams. In this episode, […]
Episode 181: AI Zero-Days (Google Threat Intelligence Report)
Google’s Threat Intelligence Group just dropped a game-changing report on the role of AI in modern cyber attacks. In this episode, we break down what’s […]
Episode 180: Cybersecurity Echo Chambers — How to Think Critically in a Hype-Driven Industry

In this episode, we break down the dangers of echo chambers in cybersecurity and the importance of critical thinking in a hype-driven industry. Learn practical […]
Episode 179: OWASP Top 10 Part 1 – Broken Access Control, IDOR, and CORS Explained
Get up to speed on the latest OWASP Top 10 as we break down key web application security categories and real-world vulnerabilities. In this episode, […]
Episode 178: Internal Security Controls That Actually Frustrate Attackers
Internal security controls can make or break your ability to stop attackers in their tracks. In this episode, we break down the practical controls that […]
Episode 177: Claude Mythos — What It Does, What It Doesn’t, and What Your Organization Should Do Now

Claude Mythos found tens of thousands of vulnerabilities in some of the world’s most critical software — including a 20-year-old flaw in BSD — and […]
Episode 176: Cybersecurity Advice That Fails
In this episode of the Cyber Threat Perspective podcast, Brad and Spencer call out the cybersecurity advice that gives organizations false confidence — and break […]
Episode 175 – NetTools: The Free Active Directory Swiss Army Knife for IT Admins and Pen Testers
NetTools is one of those rare tools that replaces half your Active Directory toolkit. In this episode, Spencer and Tyler walk through how they use […]
Episode 174: Web Application Penetration Testing Tools & Techniques with Jordan

In this episode host Brad Causey sits down with web app pen testing expert Jordan Natter to walk through the tools and Burp Suite Pro […]
Episode 173: How to Find Insecure Active Directory Permissions with ADeleg
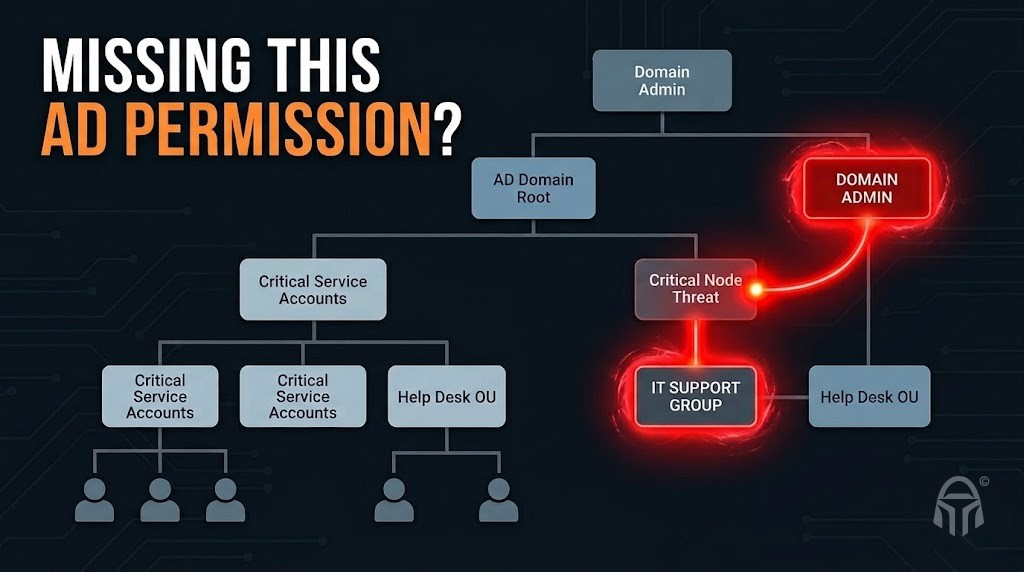
Get a fast, practical overview on using Adeleg to find insecure Active Directory permissions. In this episode, Spencer and Tyler break down how this lightweight […]